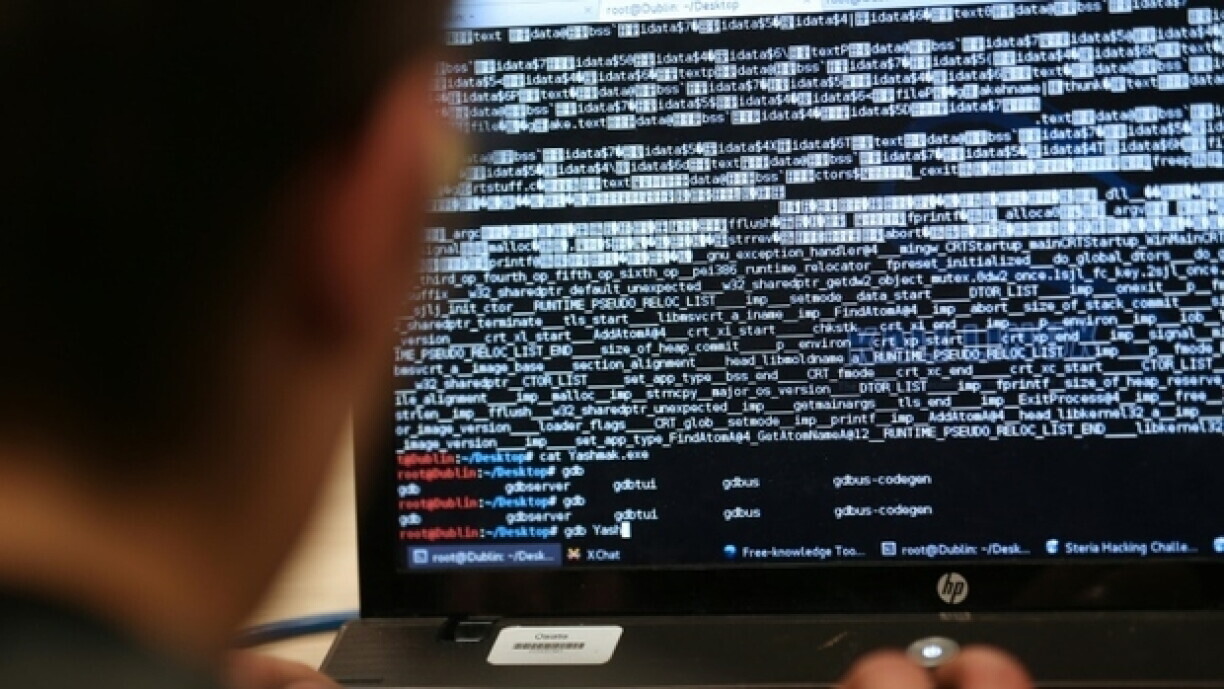
The developers behind PHP, one of the world's most popular programming languages for web development, issued a warning on Wednesday regarding two critical vulnerabilities.
These security flaws made it possible for hackers to execute malicious code on web servers without needing a username or password, putting countless sites at risk.
According to Pascal Steichen, Director of the Luxembourg House of Cybersecurity (LHC), the scale of the issue is significant. PHP is used to build up to 70% of all websites globally, and in Luxembourg alone, well over 5,000 sites rely on it.
As a precaution, many websites were temporarily taken offline until administrators could apply the necessary security updates.
For most users, the only visible effect would have been brief website outages. However, Steichen warned that, in the worst-case scenario, entire sites could have been taken over by cybercriminals.
While the update process itself takes just a few minutes per site, the sheer number of affected websites means it could be some time before the threat is fully eliminated.
In response to these PHP vulnerabilities, the Cyber Risk Assessment Cell (CERC) recommended that organisations install the latest security updates as quickly as possible. As a precaution, the Government IT Centre (CTIE) temporarily took several state services offline.
The CERC convened for a follow-up meeting on Wednesday evening after the publication of the PHP security patches.
The Luxembourg Computer Security Incident Response Teams (CSIRT) had already contacted organisations within their respective communities to inform them about the risks and to urge rapid application of the updates or, if immediate installation was not possible, to implement suitable protective measures.
CERC reiterated its recommendations and called on all operators of systems using PHP to apply the published security patches as soon as possible.
In cases where the updates cannot be installed immediately, operators are advised to carry out a risk assessment, take appropriate compensatory measures, and, if necessary, temporarily disable exposed systems to reduce the risk of exploitation.
Organisations should also check whether their systems may have been compromised and contact their designated CSIRT for assistance if required.
The government acted swiftly to implement precautionary measures for potentially affected government systems, with the CTIE making certain services temporarily unavailable as a preventive step.
Technical analysis is ongoing, and authorities are continuing to monitor the situation closely.
The CERC includes representatives from state High Commission for National Protection, Luxembourg Regulatory Institute (ILR), Financial Sector Supervisory Commission (CSSF), CTIE, the Luxembourg Army, Centre for Educational IT Management (CGIE), and Restena.